CYBER JACKING BY IMK
⭕🔱🇰🇦🇱🇮™🔱⭕Cyber hijacking, or computer hijacking, is a type of network security attack in which the attacker takes control of computer systems, software programs and/or network communications.
🍎IJacking
Identify theft. Situation in which attacker obtains one’s personal information, bank statements, social security number, credit card numbers, usually for financial gains.
🍎ClickJacking
Most of us, surfing/internet junkies had a situation in which we clicked on something that lead to unexpected things happening (mostly related to ads, but there were suspicious redirections) which consequently turned on panic mode.
ClickJacking tricks users into performing an action they didn’t intend to do, frequently by rendering an invisible page element on top of the action user thinks they’re perfoming. Sensitive information might be revelead, malware could be downloaded, malicious links could be opened in any case, nothing good can come of it.
There are a couple of variations of this attack:
- Likejacking
- Cursorjacking
- CookieJacking
- FileJacking
🍎CryptoJacking
Cryptojacking is malicious cryptomining that happens when cybercriminals hack into both business and personal computers, laptops, and mobile devices to install software. This software uses the computer's power and resources to mine for cryptocurrencies or steal cryptocurrency wallets owned by unsuspecting victims.
🍎Juice Jacking
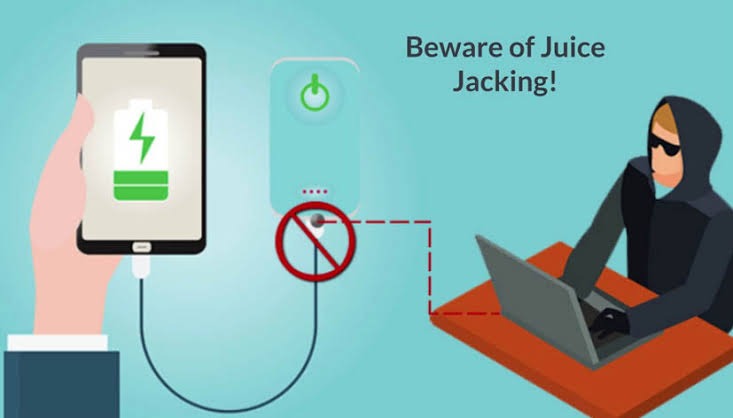
Juice jacking refers to a type of cyberattack in which they commandeer a charging port that doubles as a data connection. Essentially, cybercriminals hijack your power supply (hence “juice” jacking) channel and use it for their own nefarious deeds. They do this to install malware on a victim’s device and/or steal data. This process can include installing tracking programs and mirroring their screen to see (and record) any passwords and PIN codes they enter while the device is charging. Hence why juice jacking is also sometimes known as “juice filming” or “juice filming charging attacks.”
How would juice jacking work?
As you may have noticed, when you charge your phone through the USB port of your computer or laptop, this also opens up the option to move files back and forth between the two systems. That’s because a USB port is not simply a power socket. A regular USB connector has five pins, where only one is needed to charge the receiving end. Two of the others are used by default for data transfers.
Types of juice jacking
There are two ways juice jacking could work:
- Data theft: During the charge, data is stolen from the connected device.
- Malware installation: As soon as the connection is established, malware is dropped on the connected device. The malware remains on the device until it is detected and removed by the user.
Safety Measures
Detecting malware on your device:
Here are some signs indicating that your device may be infected with malware:
- A surge in monthly data usage: Sudden spikes in data without any changes in data usage patterns from your side need investigation.
- Battery draining quickly: Juice jackers may have infected your device with battery-sucking viruses. The drain will occur almost immediately after infection, so you should be able to spot this one early.
- Possible identity theft: If the attacker has managed to steal your personal information and impersonated you for financial gains, you may see withdrawals from your bank account that you cannot explain, see unfamiliar charges or accounts on your credit report, or not get your usual bills.
- Unwanted apps: Android phones and jailbroken iPhones, when infected with Trojan malware, will automatically download more malicious apps without your knowledge.
- Check running services of your device in developer option.
🍎Web Jacking
Illegally seeking control of a website by taking over a domain is know as Web Jacking. In web jacking attack method hackers compromises with the domain name system (DNS) that resolves website URL to IP address but the actual website is never touched.
Web Jacking Attack Method:
- The first step of web jacking attack method is to create a fake page of victim website for example www.anywebsite.com/login.php.
- The second step is to host it either on your local computer or shared hosting.
- The third step is to send the link of a fake page to the victim.
- The fourth step victim will open the link and enter their details and submit.
- Last step, you will get all the details submitted by victim.
How to apply web jacking attack method:
- Step-1:
- So to apply web jacking attack method we will use a tool in kali linux called setoolkit.
- Step-2:
- Open your kali linux operating system, and then open Terminal window.
- Step-3:
- Type setoolkit on the terminal.
- Step-4:
- It will display lots of attacking method but you have to select Social-engineering attack.
- Step-5:
- Type 1 to select Social-engineering attack, it will display lots of social engineering attack method. Here, you have to select website attack vector, so type 2, it will display different website attack method.
- Above methods will create a fake website page same as victim website page and host it on your computer.
- Step-6:
- Copy the link(your computer IP which you entered previously) of fake website and send it to the victim. If the link is your local computer IP address then convert it into domain name. To convert your IP address in domain name, open the link and type your computer IP address here, it will create a link. Now, your link is ready copy it and send it to the victim and wait till he/she entered their details.
- Step-7:
- When a victim will open the link in their browser, the browser display the message “the site www.abc.com has move on another address, click here to go to the new location” and if the victim clicks on this link he will get redirected on the fake webpage.
How to be safe from web jacking attack method !
- First of all do not enter sensitive data in any link sent to you.
- Check the URL
- Just because the address looks Ok, don’t assume this is a legitimate site.
- Read company name carefully, is it right or wrong.
- check that there is http protocol or https, if http then do not enter your data.
- If you are not sure, site is real or fake, enter a wrong username and password.
- Use a browser with antiphising detection
🍎FormJacking
A type of virtual ATM skimming, the Cyber criminals inject malicious code into retailers’ websites to steal shoppers’ payment card details. An average more than 4800 websites are compromised with formjacking attack in a month.
How does FormJacking Work?
1. Attacker injects malicious script into targeted web page.
2. User loads web page and fills in form to make purchase.
3. When users submit the form to complete a purchase the form data us sent to the merchant website.
4. A copy of the form data, including payment card details, is also sent to the cyber attacker.
🍎WiFi-Jacking
An attack in which attackers accesss neighbor’s WiFi without any form of cracking, relying on saved browsers creadentials which are reused again for the same URL. Certain pre-requisites need to be met.
- active client device on the target network
- client device have previously connected to any other network (with automatic reconnection)
- client device is using Chrome or Opera
- client device have router admin interface credentials remembered by the browser
- target’s router admin interface has to be configured over unencrypted HTTP
New browser versions have been patched.
🍎BrandJacking / Reputationjacking
BrandJacking is a type of forgery, exploiting the trademarks of well-known companies to trick victims and gain their trust. For e.g. fake invoice notifications or requests for account verification.Which mainly carders (scammers) do on telegram and other social platforms to generate fake delivery receipts and payment screenshots.
Some of the most common brandjacking methods are:
- Squatting: When an entity registers domain names similar to those of the main brand to create fake websites.
- Social media: When an entity creates fake social media accounts and posts content pretending to be you.
- Adwords: When an entity places higher bids on keywords relevant to your brand and eats into your organic traffic.
🍎SideJacking
SideJacking is the process of stealing someones’s access to a website via session cookies (session hijacking). Most fequently on unsecured public WiFi connections. Attacker basically sniffs out the packets containing “session cookies” and using that information to access victims account.
HTTPS/HSTS makes this a bit difficult to execute, but there are still vast number of sites that don’t use it. Once the user logs out, session is destroyed (attacker loses access), so it’s a good idea/practice to always logout.
🍎HyperJacking
A hypervisor, also known as a virtual machine monitor or VMM, is software that creates and runs virtual machines (VMs). A hypervisor allows one host computer to support multiple guest VMs by virtually sharing its resources, such as memory and processing.
There are two types of hypervisors:
Type-1, native or bare-metal hypervisors, run directly on the host’s HW to control HW and manage guest OSs.
Type-2 or hosted hypervisors, run on a conventional OS. A guest OS runs as a process on the host. So, we here have an abstract guest OSs running on the host OS (VMWare, VirtualBox, etc).
Rare due to difficulty, but considered as a real-world threat.
🍎PageJacking
PageJacking is basically a process of illegaly copying website content/pages to another website in order to direct traffic from the original site to a cloned one. People behind this rely on search engines to index clones, mixing the pages with the original website. Users are deceived into believing that a cloned website is the real one. Further actions might be some redirections to unwanted content or worse.
🍎TabJacking / TapJacking
TabJacking (TabNabbing) is somewhat confusing term.One definition states that it enables attackers to inject malicious code into the tabs of your browsers, worms, trojans, simply taking control, using them for marketing activities and advertising, etc. Other definition simply states it’s a type of phishing attack in which one tab after period of inactivity changes its content. For e.g. person can open some website in one browser tab and than switch to another. First tab can detect a period of inactivity and replace the content, for instance it can now show gmail login page. Uppon return, inexperienced users might be deceived/tricked and end up entering login credentials (not noticing the URL is not the right one).
TapJacking is same/similar, deceiving users to click/tap on something they did not intend to click on. For e.g. screen overlays (TYPE_APPLICATION_OVERLAY), are windows drawn on top of other apps. User might think he’s interacting with overlay but in reallity he’s performing actions in the underlying app. This way, user can be tricked into enabling certain permissions or changing some dangerous settings.
🍎BioJacking [BrainJacking / HeartJacking / BionicJacking]
There are many terms related to hacking an implanted medial device, so it’s best if we merge them all under one term we “invented”, BioJacking. Yes. we’re in that age. Future is here.
Brain neuroimplants are used to treat wide range of conditions (Parkinson’s, chronic pain, depression,etc. Wireless communication can potentially be intercepted and implants reprogrammed. Attackers could affect target’s psychological state or with some implants maybe even paralyze them for a while. Applications are endless. Attacker could affect some businessman to make a wrong decision if they turned off implant that manages depression, or can immobilize someone driving a car.
Bionics are constantly being developed, some read muscle impulses other communicate directly with the brain, and as with previous situations we mentioned, bionic hacking is a possibility. Attackers could hack a bionic leg setting it to malfunction when person is on top of the stairs, or maybe forcing bionic arm to stab the owner when he’s holding the knife in the kitchen.
Unfortunatelly, medical companies and clinics are not setting high priority on security, counting on probability/likelihood of something like that happening, questioning the motives on why would someone do such things. They’ll most certainly work on improvements, but overall, scary s***.
🍎PasteJacking
Pastejacking (Clipboard poisoning) is a method that malicious websites employ to take control of your computers’ clipboard and change its content to something harmful without your knowledge.
Usual example is situation in which user copies some terminal commands from a tutorial on some website, pasting it into his local terminal, but instead of those commands, malicious commands get copied to clipboard too. Malicious part get executed first, screen gets cleared and then copied terminal commands get executed afterwards. User doesn’t see the difference, but in the background for instance meterpreter session got opened.
🍎MetaJacking
Attacker stealing the content of another high ranking website’s HTML Meta tags (page description, keywords, etc) in order to place his own website higher in a search engine’s results.
🍎ThreadJacking
The simple act of taking over an email list or discussion thread with a subject unrelated to the original posting.
🍎MouseJacking
Exploiting wireless, non-Bluetooth keyboards and mices to take control over the victim’s computer. Can be used to perform malicious activitis, typing arbitrary text, sending commands, sniffing, etc.
🍎TrendJacking / NewsJacking / DateJacking
TrendJacking/NewsJacking is basically attention hijacking. Taking advantage of current events and news stories in order to promote one’s idea, product or brand by injection them into one’s news and reports.
Compared to dynamic nature of NewsJacking, DateJacking is similar, but it focuses on well known, popular, celebrated events and dates. It definitely provides enough time to prepare the content and strategy.
🍎DataJacking
DataJacking is a trend of going after corporate data in production environments. It can definitely be categorized as a type of ransomware
Four steps to take to prevent data jacking:
❤️Put strong security measures in place when using third-party or open source software. It is worth noting that the default installation of MongoDB does not require authentication to access the database—a real security risk.
❤️Test your systems more than once a year. Is everything working properly? Are there any security holes that might have popped up? Testing doesn’t just provide benefits to your disaster recovery system, it’s good for your production as well.
❤️Limit app permissions. Do you really need your health app to access your contacts? The more data you give an app permission to see, the more you put yourself at risk should it be compromised.
❤️Ensure secure, encrypted phone messaging. Employees don’t regularly worry if their communications are secure. If you automatically enable encrypted messaging on work devices, you won’t have to worry about it, either.
I hope you all like this post, thankyou.
For more=@ITS_ME_KALI
#staysafe #staylegal #imk